Security
authorization (authZ)
what you may do
Source board
This definition comes from the board below. Open it to see the term in context.
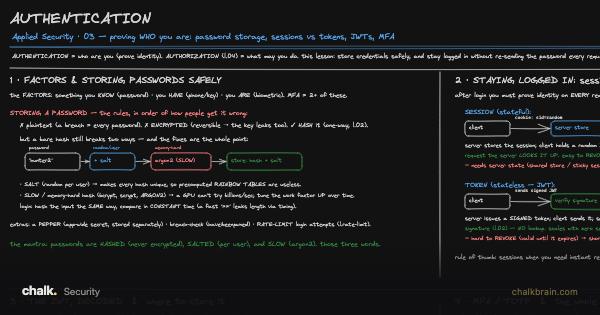 AuthenticationSecurity
Also defined on Authorization and Identity.
More terms from this board
- authentication (authN)prove who you are
- bcrypt/scrypt/argon2slow, memory-hard password hashes
- factorsknow/have/are
- httpOnly / Secure / SameSitecookie flags (XSS-safe / HTTPS-only / CSRF-blocking)
- MFA2+ factors
- pepperapp-wide secret added before hashing
- rainbow tableprecomputed hash→password lookup
- refresh tokenre-issues short-lived access tokens
- saltrandom per-user value defeating rainbow tables
- sessionserver-side state + a cookie id (revocable)
- token/JWTstateless signed credential (scales, hard to revoke)
- TOTPtime-based one-time code (HMAC of the clock)
- WebAuthn / passkeysphishing-resistant hardware auth
- work factortunable slowness