Security
IDOR
accessing another user's object by changing an id (authN-but-not-authZ)
Source board
This definition comes from the board below. Open it to see the term in context.
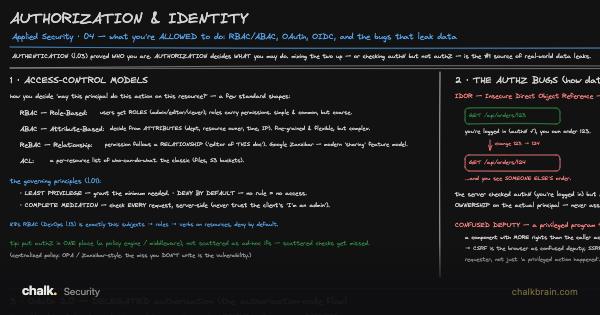 Authorization and IdentitySecurity
More terms from this board
- ABACattribute-based
- access tokenAPI access (authZ)
- ACLper-resource permission list
- confused deputya privileged component tricked into acting for someone (CSRF/SSRF)
- ID tokenwho the user is (authN)
- OAuth 2.0delegated authorization (scoped ACCESS TOKEN, no password shared)
- OIDCOAuth + an ID TOKEN (authentication / 'login with…')
- RBACrole-based
- ReBACrelationship-based (Zanzibar)
- scopea token's permission