Security
input validation
check untrusted input at the boundary
Source board
This definition comes from the board below. Open it to see the term in context.
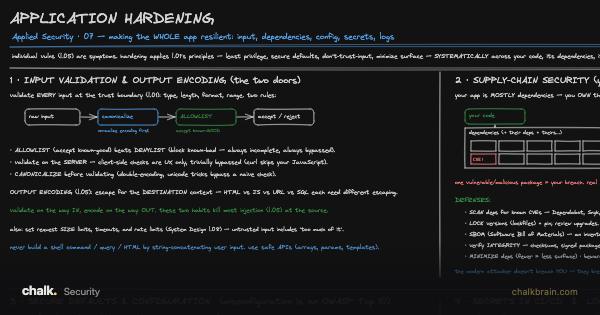 Application HardeningSecurity
More terms from this board
- allowlist vs denylistaccept-known-good vs block-known-bad
- canonicalizenormalize before checking
- CVEa known published vulnerability
- fail securelydeny + generic error on failure
- hardeningl.01 principles applied everywhere
- lockfilepinned dependency versions
- masked variablehidden in logs
- OIDC-to-cloudshort-lived CI creds, no static keys
- SAST/DASTstatic / dynamic app security testing
- SBOMsoftware bill of materials
- secret scanningdetect committed keys (trufflehog/gitleaks)
- security headersCSP/HSTS/X-Frame-Options/nosniff
- security misconfigurationunsafe defaults/settings (OWASP)
- SLSA/sigstorebuild provenance & signing
- supply chainyour dependencies (+transitive)