Security
the universal cure
separate data from code + validate/allowlist + least privilege (l.01) + defense in depth
Source board
This definition comes from the board below. Open it to see the term in context.
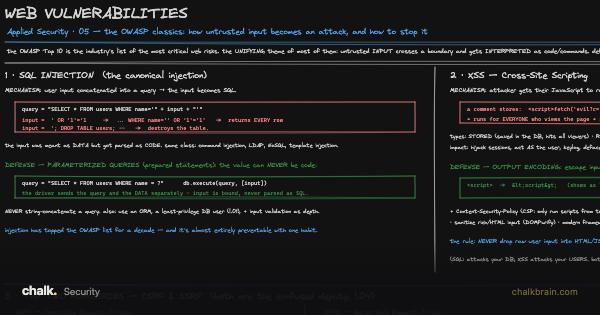 Web VulnerabilitiesSecurity
More terms from this board
- cloud metadata endpoint169.254.169.254
- CSPContent-Security-Policy (restrict script sources)
- CSRFyour browser tricked into an authenticated request (fix: CSRF token / SameSite)
- injectionuntrusted input parsed as code
- output encodingescape input to render as text
- OWASP Top 10the canonical web-risk list
- parameterized query / prepared statementbind data separately from the query (the fix)
- sanitizationstrip dangerous markup
- SQL injectioninput becomes SQL
- SSRFyour server tricked into fetching an internal URL (fix: allowlist, block metadata IP)
- XSSattacker JS runs in a victim's browser (stored/reflected/DOM)