The door you forgot was a door (fail-open checks and logic bugs)
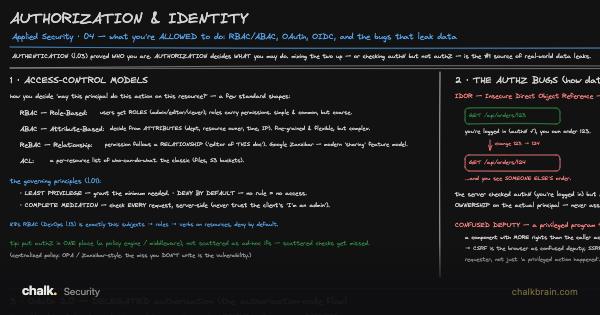
What you are allowed to do, and the bugs that leak data. Two of its rules carry this lesson: deny by default (no rule means no access) and check every request on the server, never trusting the browser’s word. The bugs below are what happens when one of those rules has a gap nobody drew.
Before you start. Authorization & Identity taught the ownership check: logging in proves who you are, not that order 124 is yours. Web Vulnerabilities (the OWASP classics) taught the bugs where an attacker’s text becomes code. Review the fix (secure code review) had you review a dozen fixed handlers, including a form that accepted a field it never meant to. This lesson is about bugs where nobody’s text becomes code and every line looks right: the door is a situation the code never planned for.