The key that has to change (secrets and key management)
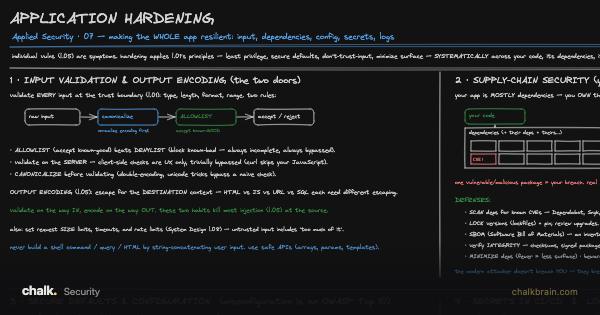
Every place in an app where a habit keeps it safe. One of them is the note taped inside the drawer: the password or key that ends up somewhere a wider audience can read. This lesson is that drawer, opened: where secrets should live, how to lock data so a stolen disk is useless, and how to change a key without stopping the app.
Before you start. Cryptography Foundations gave you symmetric encryption: one secret key locks and unlocks, so whoever holds the key holds the data. Application Hardening said secrets belong in a locked store and never in a config file or a log, without saying how that store works. That is where this lesson starts.