IAM & Identity
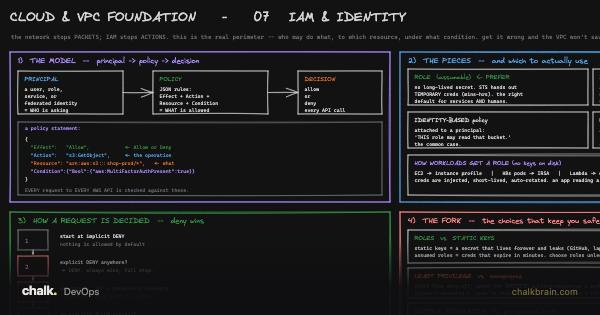
The guard that checks every single action, drawn as one flow with a fixed order of questions. It states the headline right: one explicit “no” beats any number of “yes”es. The flow it draws is correct for one account acting inside itself; this lesson is that guard’s rulebook written out properly, plus what changes the moment two accounts are involved.
Before you start. AWS Identity and Access Management (IAM) is the part of Amazon Web Services that decides who may do what, and it keeps two things apart: who you are and what you may do. Who you are is your login, the identity AWS knows you as once you’re signed in; this note calls that your badge. What you may do is written down in a policy, a list of allowed actions. You attach that list to one person, to a group of people, or to a role, a hat a program or a person puts on for a while and takes off again. Why So Many Boxes? - Identity vs Permission explains why AWS splits things this way, and The Badge Machine - IRSA end to end and OIDC - the Passport & the Stamp-Book how a badge gets handed out; you need none of them first. This note asks one narrower question: when several attached lists all have an opinion about the same request, which one wins.